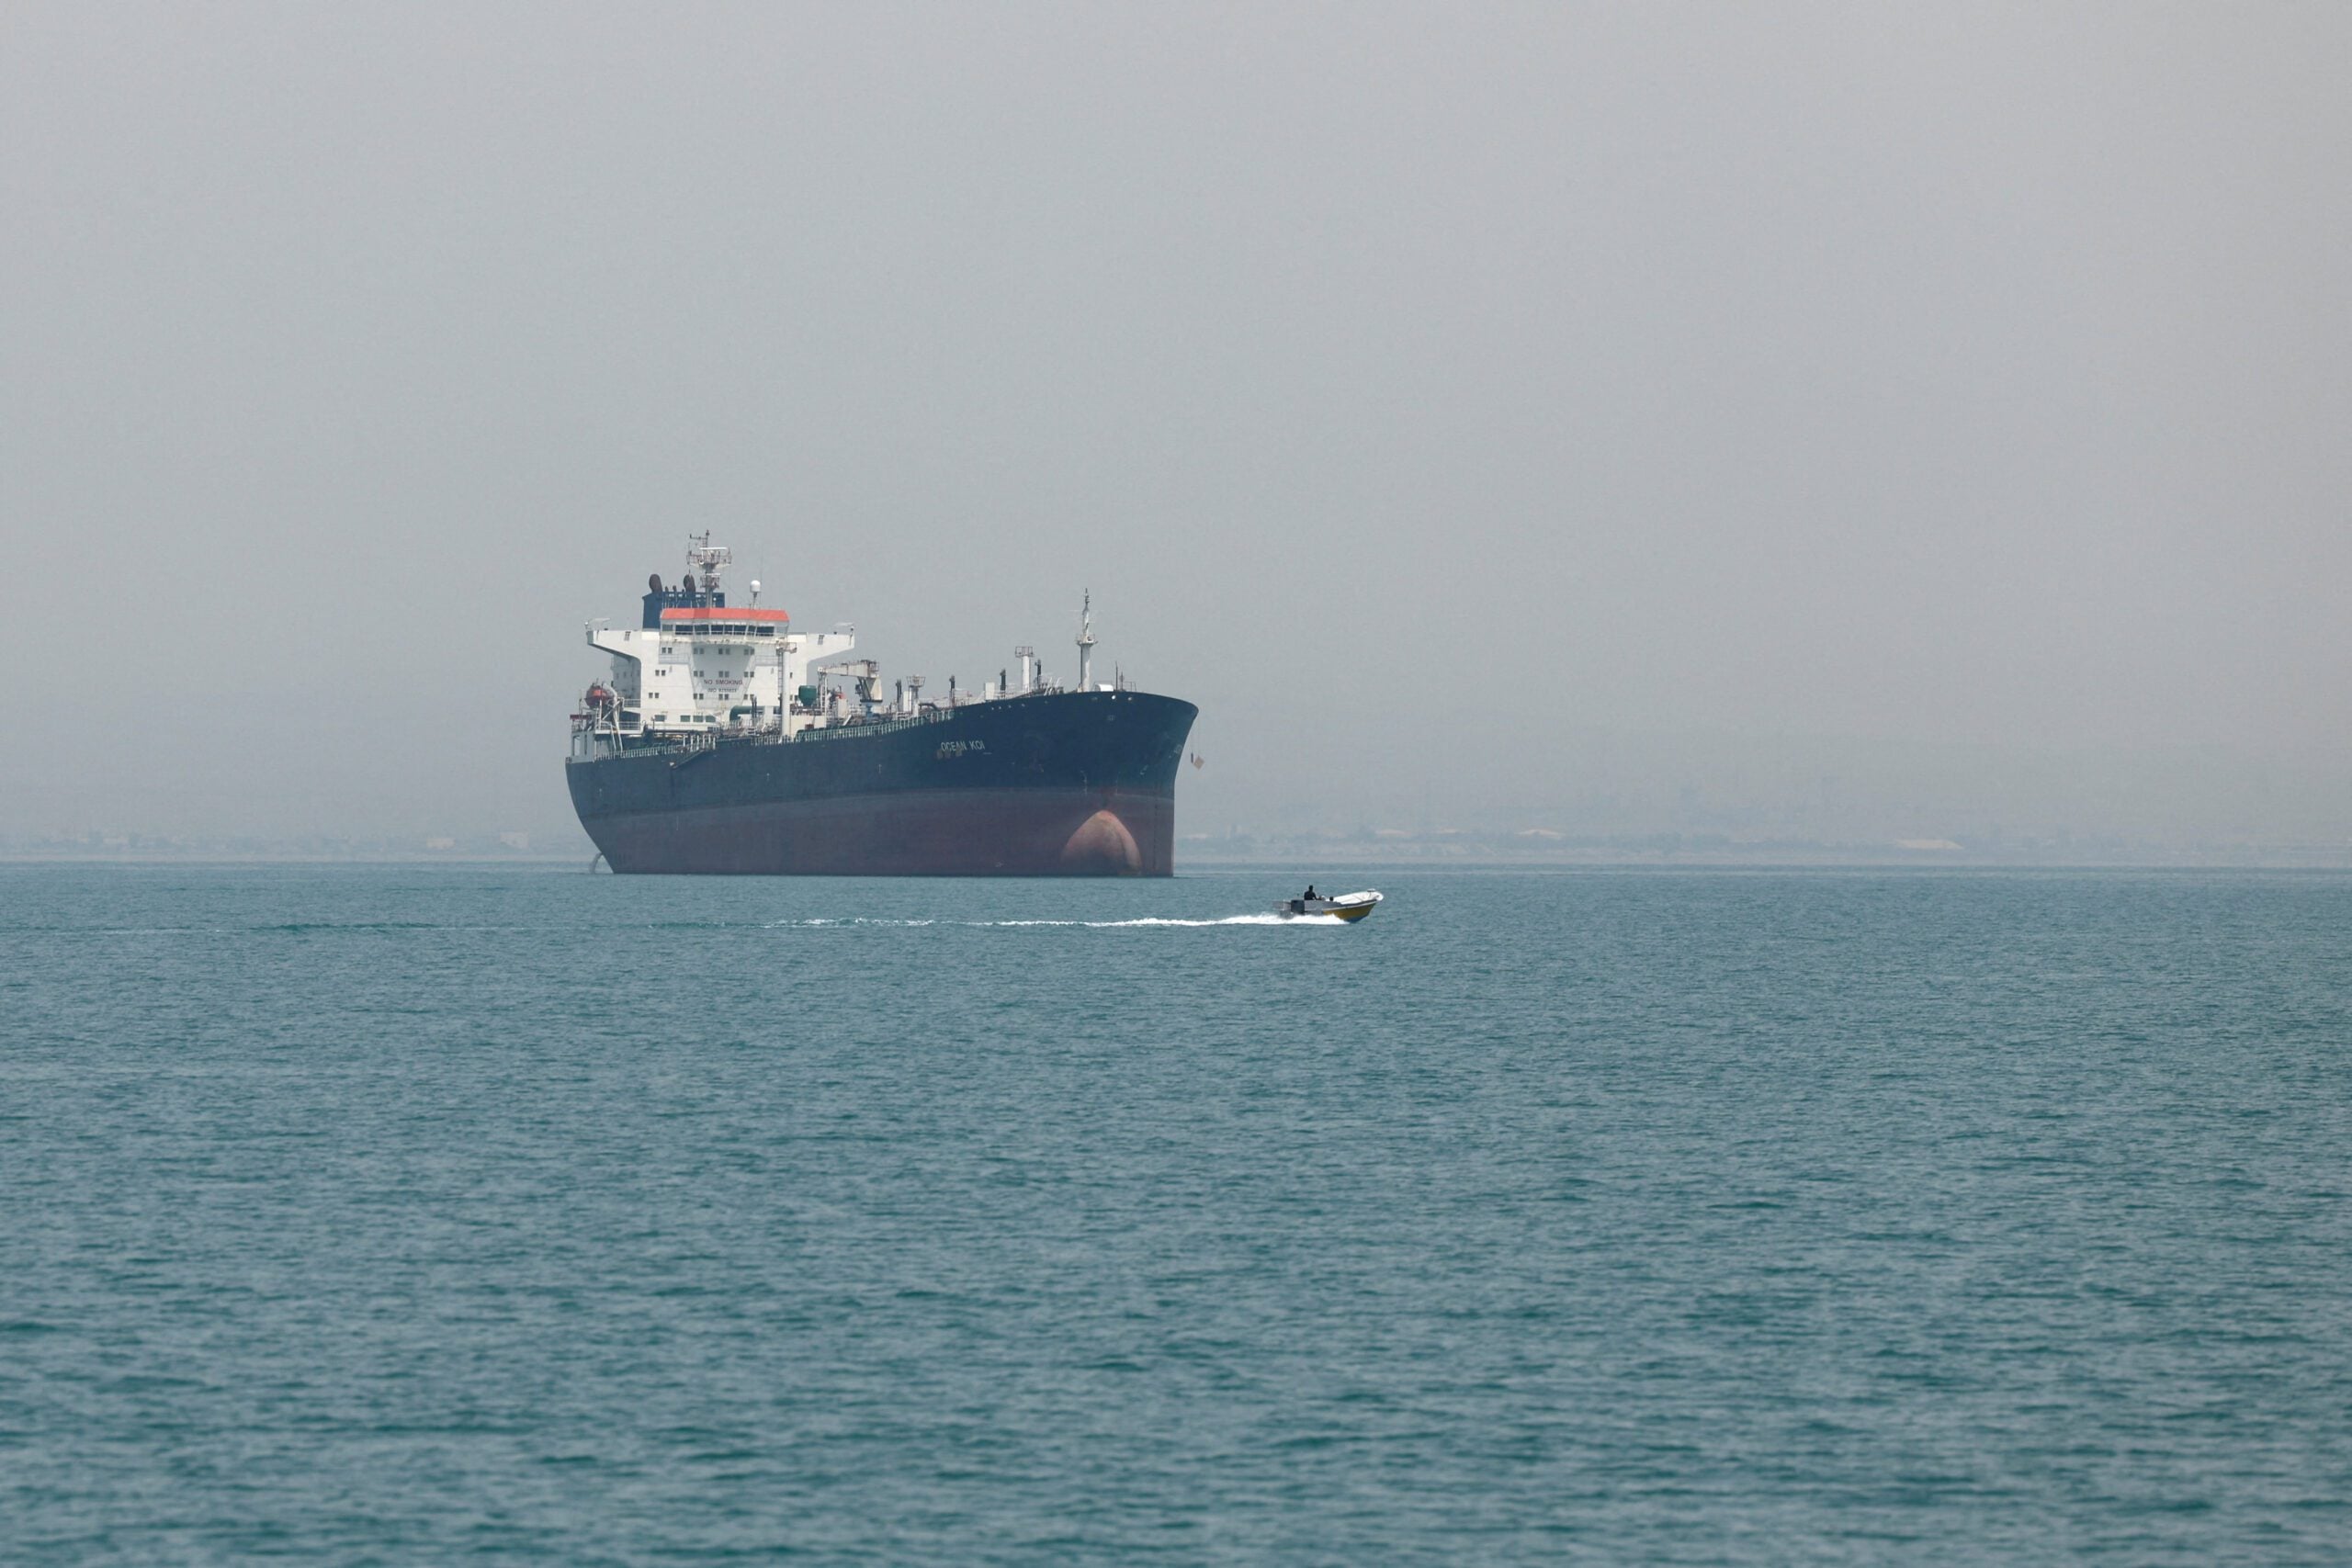
By Paul Morgan (gCaptain) – October has become the worst month on record for attacks on merchant ships in and around the Strait of Hormuz, and oil is now washing onto the beaches of the United Arab Emirates.
The engineering question that follows is uncomfortable: were the ships under fire ever designed, equipped or crewed to survive what is happening to them?
On 23 October, Reuters reported data from the Washington Institute for Near East Policy recording 28 confirmed and reported attacks in the Strait and surrounding waterways during October, and 113 since the US-Israeli war with Iran began on 28 February. The institute has tracked maritime security incidents worldwide since 2017, and October tops its records.
The IMO’s own list records around 120 incidents in the Strait and the wider Middle East since the conflict started, while UKMTO had logged 135 conflict-related incidents by 16 October. The totals differ because coverage and methods differ, and UKMTO reporting is voluntary, but the direction of travel is beyond dispute.
The damage to the tanker fleet is striking. A Reuters review of IMO and MarineTraffic data found that more than 30 very large crude carriers had been damaged, including 11 in October alone, equivalent to around 3.5% of the world’s VLCC fleet. Greek risk consultancy Marisks counted a dozen ships attacked between 5 and 11 October, the highest weekly total of the conflict.
The human cost has been heavy. By September the IMO counted at least 22 seafarers killed in 80 verified attacks around Hormuz since the end of February. Five more died after an attack on the Honour 25 off Somalia, from which survivors were rescued on 29 September, a reminder that the danger is no longer confined to one strait.
Commercial pressure keeps ships moving into harm’s way. Reuters reported daily freight rates above $1 million drawing tonnage to load inside the Gulf, even as IMF PortWatch recorded only four transits of the Strait on 18 October against a pre-war average of around 85 a day. Every one of those transits is a crew betting on probability.
The stakes explain why ships keep coming. The Strait normally carries around a fifth of the world’s seaborne oil and LNG, and each laden VLCC holds roughly two million barrels. That concentration of value and hazard in a narrow waterway makes it an ideal target, and it means every successful strike carries an environmental as well as a human price.
Then came the pollution. On 23 October, the UAE Ministry of Climate Change and Environment confirmed that teams were containing oil leaking from a tanker offshore. Umm Al Quwain closed its beaches and coastal areas, Sharjah closed Al Hamriya beach as a precaution, and the following day Ras Al Khaimah shut all of its beaches until further notice. There is also reports of oil pollution on some of the beaches!
The ministry did not name the vessel or confirm the cause. International maritime agencies have identified it as the Gem No.2, a 330-metre tanker struck in a suspected drone attack on 9 or 10 October, from which 22 Indian seafarers were rescued. A European Space Agency radar image from 21 October showed oil leaking from a tanker about 25 kilometres off Umm Al Quwain.
The IMO had already taken a political position. At MEPC 84 in the spring, member states adopted resolution MEPC.406(84), strongly condemning Iran’s attacks on merchant vessels in the Gulf and Strait of Hormuz region. Condemnation, however, does not seal a ruptured cargo tank, and the engineering consequences now landing on UAE beaches demand an engineering response.
It is worth asking what the international safety framework was built to do. SOLAS fire protection, detection and extinction requirements were developed largely around accidental fires: a leaking fuel pipe on a hot exhaust, an electrical fault, a cargo fire. The design assumption is an internal event, detected early, contained by structural boundaries and fought with intact systems.
An external strike breaks every link in that chain at once. A missile or drone can breach structural fire boundaries, rupture fuel and cargo lines, sever cable runs and damage fire mains in a single instant. Fixed systems may be compromised before anyone reaches a release station, and the compartment designed to contain the fire may now have a hole in it.
Electrical power is often the decisive weakness. Emergency generators, switchboards and their cabling are deliberately separated from main machinery spaces, but separation designed against an engine room fire may not survive blast and fragments. Loss of power means loss of fire pumps, ventilation control, steering and lighting at precisely the moment every one of them is needed.
Fuel isolation is another vulnerability. Quick-closing valves and remote shutdowns work only if their air, hydraulic or electrical controls survive the initial damage. On a tanker, holed cargo tanks can add flooding, progressive leakage and stability concerns to the fire, forcing a crew trained to handle one emergency at a time to manage three simultaneously.
The ISM Code requires companies to identify potential shipboard emergencies and to establish procedures, drills and exercises to respond to them. In principle, that obligation already covers attack damage. In practice, many safety management systems still treat fire, flooding and blackout as separate scenarios with separate checklists, rarely rehearsed together.
The ISPS Code, adopted in the aftermath of the September 2001 attacks, was built largely around preventing unauthorised access, stowaways and terrorism through security assessments, access control and security levels. It was never intended to tell a chief engineer how to restore power after a projectile has passed through the funnel casing.
That leaves a gap between security planning and damage control. Navies spend generations learning to fight fire, flooding and structural damage together, with zoned systems, redundancy and crews drilled to the point of instinct. Merchant ships carry a fraction of the crew, no dedicated damage control parties and equipment sized for accidents, and nobody should pretend otherwise.
Nor is turning tankers into warships the answer. The cost would be prohibitive and the principle wrong, because the protection of merchant shipping is ultimately the responsibility of states. However, there is a substantial middle ground between doing nothing and armour plating, and much of it lies within the gift of owners, managers and their technical departments.
Combined-casualty drills are the obvious starting point. Crews should rehearse a scenario in which fire, flooding and loss of main power occur together, with key personnel deemed injured and a primary control position deemed lost. Such drills are uncomfortable and often exposing, which is exactly why they are so valuable.
Engineering reviews should follow. Technical departments can examine the routing of emergency power cables, the location and protection of emergency fire pumps, the independence of local controls for quick-closing valves, and whether portable pumps, smoke extraction and hull patching materials are carried in quantities sized for damage rather than routine leaks.
Pollution response must sit within the same plan. A crew fighting to save a ship should know which tanks can be isolated, how cargo can be transferred within the hull, and how quickly salvage and pollution response can realistically arrive in a war zone where tugs and response vessels may themselves be targets.
Gas carriers, chemical tankers and ships carrying dangerous goods deserve particular attention. A breached LPG or chemical cargo presents hazards to the crew and to surrounding coastlines that a crude spill does not, and emergency plans written for collision or grounding may not reflect the speed and violence with which an attack can escalate.
Crew welfare is part of resilience too. Seafarers working under the constant threat of attack carry fatigue and stress that degrade decision-making precisely when clear thinking matters most. Rest management, honest briefings and genuine freedom to refuse unsafe passages are not soft extras; they are conditions for a crew able to fight for its ship.
Abandonment presents its own dilemma. Lifeboats and liferafts are designed for a ship that is sinking or burning, not one that may be struck again while crews are mustering. Masters need clear company guidance on when to abandon, when to shelter in a protected space, and how to communicate their position when satellite positioning itself may be unreliable.
Regulators have a role as well. Flag states and classification societies could usefully share anonymised damage data from this conflict, showing which systems survived, which failed and why. The industry learned hard lessons during the tanker war of the 1980s, much of that knowledge has faded, and it should not have to be relearned at the cost of further lives.
The SOLAS, ISM and ISPS framework remains sound for the world it was designed for, and most ships will never face a missile. But the ships in the Gulf this autumn are facing exactly that, and their crews deserve emergency arrangements tested against the threat in front of them rather than the one imagined when the rules were written.
Ships were built to survive the sea. This year has shown that some must now be prepared to survive the people on it, and the time to plan for that is before the next alarm sounds, not after.
 Join The Club